Computer SecurityComputer Security
How we keep data secret, safe, and trusted — ciphers, keys, hashes, and defenses. Data কীভাবে গোপন, নিরাপদ আর বিশ্বাসযোগ্য রাখা হয় — cipher, key, hash আর defense।
- Basic CryptographyBasic Cryptography
- Symmetric EncryptionSymmetric Encryption
- Asymmetric Encryption (RSA, Diffie-Hellman)Asymmetric Encryption (RSA, Diffie-Hellman)
- Hashing & Digital SignaturesHashing & Digital Signatures
- Authentication & Access ControlAuthentication & Access Control
- Common Network & Security ConceptsCommon Network & Security Concepts
- Practice QuestionsPractice Questions
1. Basic Cryptography1. Basic Cryptography
What is security about? The CIA triad
Computer security has three main goals. Together they are called the CIA triad.
- Confidentiality — only the right people can read the data. Example: your exam result should be visible only to you, not to strangers.
- Integrity — the data is not changed by anyone in a wrong way. Example: nobody should be able to change your bank balance from 5000 to 500.
- Availability — the system works when you need it. Example: the bank website should be up when you want to pay a bill.
Every attack breaks at least one of these. Reading someone's private email breaks confidentiality. Changing a file secretly breaks integrity. Crashing a server breaks availability.
Security আসলে কী নিয়ে? CIA triad
Computer security-র তিনটা মূল লক্ষ্য আছে। একসাথে এদের বলে CIA triad।
- Confidentiality — শুধু সঠিক মানুষই data পড়তে পারবে। যেমন: তোমার exam result শুধু তুমি দেখবে, অপরিচিত কেউ না।
- Integrity — data কেউ ভুলভাবে বদলাতে পারবে না। যেমন: কেউ যেন তোমার bank balance 5000 থেকে 500 করে দিতে না পারে।
- Availability — দরকারের সময় system কাজ করবে। যেমন: bill দিতে গেলে bank website চালু থাকবে।
প্রতিটা attack এই তিনটার অন্তত একটা ভাঙে। কারো private email পড়া মানে confidentiality ভাঙা। গোপনে file বদলানো মানে integrity ভাঙা। Server crash করানো মানে availability ভাঙা।
Basic terms
- Plaintext — the original readable message. Example: "HELLO".
- Ciphertext — the scrambled, unreadable message. Example: "KHOOR".
- Key — the secret value used to scramble and unscramble.
- Encryption — plaintext + key → ciphertext.
- Decryption — ciphertext + key → plaintext.
- Cryptanalysis — trying to break a cipher without knowing the key.
In math form, with encryption function \(E\) and decryption function \(D\):
Basic term গুলো
- Plaintext — আসল পড়ার মতো message। যেমন: "HELLO"।
- Ciphertext — এলোমেলো, পড়া যায় না এমন message। যেমন: "KHOOR"।
- Key — যে গোপন value দিয়ে message এলোমেলো করা আর ফেরত আনা হয়।
- Encryption — plaintext + key → ciphertext।
- Decryption — ciphertext + key → plaintext।
- Cryptanalysis — key না জেনে cipher ভাঙার চেষ্টা।
Math আকারে, encryption function \(E\) আর decryption function \(D\) হলে:
Caesar cipher — the simplest cipher
The Caesar cipher shifts every letter by a fixed number. With shift \(k\), letter position \(P\) becomes:
Caesar cipher — সবচেয়ে সহজ cipher
Caesar cipher প্রতিটা letter-কে নির্দিষ্ট সংখ্যক ঘর সরিয়ে দেয়। Shift \(k\) হলে letter-এর position \(P\) হয়ে যায়:

- H (7) → \( (7+3) \bmod 26 = 10 \) → K
- E (4) → \( (4+3) \bmod 26 = 7 \) → H
- L (11) → \( (11+3) \bmod 26 = 14 \) → O
- L (11) → O
- O (14) → \( (14+3) \bmod 26 = 17 \) → R
- H (7) → \( (7+3) \bmod 26 = 10 \) → K
- E (4) → \( (4+3) \bmod 26 = 7 \) → H
- L (11) → \( (11+3) \bmod 26 = 14 \) → O
- L (11) → O
- O (14) → \( (14+3) \bmod 26 = 17 \) → R
- E (4) → \( (4-3) \bmod 26 = 1 \) → B
- X (23) → \( (23-3) \bmod 26 = 20 \) → U
- H (7) → \( (7-3) \bmod 26 = 4 \) → E
- W (22) → \( (22-3) \bmod 26 = 19 \) → T
- E (4) → \( (4-3) \bmod 26 = 1 \) → B
- X (23) → \( (23-3) \bmod 26 = 20 \) → U
- H (7) → \( (7-3) \bmod 26 = 4 \) → E
- W (22) → \( (22-3) \bmod 26 = 19 \) → T
Vigenère cipher (briefly)
The Caesar cipher uses one shift for all letters. The Vigenère cipher uses a keyword, so different letters get different shifts. The key repeats over the message.
Vigenère cipher (সংক্ষেপে)
Caesar cipher সব letter-এ একই shift দেয়। Vigenère cipher একটা keyword ব্যবহার করে, তাই আলাদা letter-এ আলাদা shift হয়। Key-টা message-এর উপর repeat হয়।
- H (7) + K (10) = 17 → R
- E (4) + E (4) = 8 → I
- L (11) + Y (24) = 35 mod 26 = 9 → J
- L (11) + K (10) = 21 → V
- O (14) + E (4) = 18 → S
- H (7) + K (10) = 17 → R
- E (4) + E (4) = 8 → I
- L (11) + Y (24) = 35 mod 26 = 9 → J
- L (11) + K (10) = 21 → V
- O (14) + E (4) = 18 → S
Substitution vs Transposition
Classical ciphers work in two basic ways:
- Substitution — replace each letter with another letter. The letters change, their positions stay. Caesar and Vigenère are substitution ciphers.
- Transposition — rearrange the positions of letters. The letters stay the same, their order changes. Example: write "ATTACK" in 2 columns and read column by column: A T T A C K → columns (A,T,C) and (T,A,K) → "ATCTAK".
Modern ciphers like AES mix both ideas many times (this is called confusion and diffusion).
Substitution vs Transposition
Classical cipher দুইভাবে কাজ করে:
- Substitution — প্রতিটা letter-কে অন্য letter দিয়ে বদলানো। Letter বদলায়, position একই থাকে। Caesar আর Vigenère হলো substitution cipher।
- Transposition — letter-গুলোর position ওলটপালট করা। Letter একই থাকে, order বদলায়। যেমন: "ATTACK" ২টা column-এ লিখে column ধরে পড়লে: (A,T,C) আর (T,A,K) → "ATCTAK"।
Modern cipher যেমন AES দুই idea-ই বহুবার মেশায় (একে বলে confusion আর diffusion)।
Kerckhoffs' principle
Kerckhoffs' principle: a cipher must stay secure even if the attacker knows everything about the algorithm — the only secret should be the key. Why? Algorithms leak, get published, or are reverse engineered. Keys can be changed easily; algorithms cannot. "Security through obscurity" (hiding the algorithm) is considered bad design.
Brute force attack
A brute force attack tries every possible key one by one. Defense is simple: make the key space huge.
- Caesar cipher: only 25 useful shifts → broken in seconds by hand.
- DES: \(2^{56}\) keys → breakable with modern hardware.
- AES-128: \(2^{128}\) keys → far too many to try; safe against brute force.
Kerckhoffs' principle
Kerckhoffs' principle: attacker algorithm-এর সব কিছু জানলেও cipher নিরাপদ থাকতে হবে — একমাত্র গোপন জিনিস হবে key। কেন? Algorithm ফাঁস হয়, publish হয়, reverse engineer হয়। Key সহজে বদলানো যায়, algorithm যায় না। "Security through obscurity" (algorithm লুকানো) খারাপ design ধরা হয়।
Brute force attack
Brute force attack মানে সম্ভাব্য সব key একটা একটা করে try করা। Defense সহজ: key space বিশাল করা।
- Caesar cipher: মাত্র 25টা কাজের shift → হাতে হাতেই কয়েক সেকেন্ডে ভাঙা যায়।
- DES: \(2^{56}\) key → modern hardware দিয়ে ভাঙা সম্ভব।
- AES-128: \(2^{128}\) key → try করার মতো না; brute force-এর বিরুদ্ধে নিরাপদ।
2. Symmetric Encryption2. Symmetric Encryption
The shared-key idea
In symmetric encryption, the sender and the receiver use the same secret key. Think of a box with one lock: the same key locks it and unlocks it. Alice encrypts with key \(K\), Bob decrypts with the same \(K\).
Symmetric ciphers are very fast, so they are used for encrypting big data: files, disk drives, video streams, most of the traffic on the internet.
Shared-key idea
Symmetric encryption-এ sender আর receiver একই secret key ব্যবহার করে। এক তালাওয়ালা বাক্স ভাবো: একই চাবি দিয়ে লাগানো আর খোলা হয়। Alice key \(K\) দিয়ে encrypt করে, Bob একই \(K\) দিয়ে decrypt করে।
Symmetric cipher খুব fast, তাই বড় data encrypt করতে এটাই ব্যবহার হয়: file, disk drive, video stream, internet-এর বেশিরভাগ traffic।
Block ciphers vs stream ciphers
- Block cipher — encrypts data in fixed-size chunks (blocks). AES uses 128-bit blocks. If the message is bigger, it is cut into blocks; if the last block is short, it is padded.
- Stream cipher — generates a stream of key bits (keystream) and XORs it with the data bit by bit or byte by byte. Good for live data like voice calls. Examples: RC4 (old, now broken), ChaCha20 (modern).
Block cipher vs stream cipher
- Block cipher — data-কে নির্দিষ্ট সাইজের টুকরায় (block) encrypt করে। AES 128-bit block ব্যবহার করে। Message বড় হলে block-এ কাটা হয়; শেষ block ছোট হলে padding দেওয়া হয়।
- Stream cipher — key bit-এর একটা stream (keystream) বানিয়ে data-র সাথে bit-by-bit বা byte-by-byte XOR করে। Voice call-এর মতো live data-র জন্য ভালো। যেমন: RC4 (পুরনো, এখন broken), ChaCha20 (modern)।
DES — a brief history
DES (Data Encryption Standard) was the US standard from 1977. It is a block cipher: 64-bit blocks, 56-bit key, 16 rounds of mixing (a Feistel structure). By the late 1990s, computers became fast enough to brute force \(2^{56}\) keys — a special machine broke DES in days. A patch called 3DES (Triple DES) runs DES three times with different keys, but it is slow. So a new standard was chosen.
AES — the current standard
AES (Advanced Encryption Standard), chosen in 2001 (the Rijndael algorithm), is today's standard block cipher.
- Block size: always 128 bits.
- Key sizes: 128, 192, or 256 bits.
- Rounds: 10 rounds (128-bit key), 12 rounds (192-bit), 14 rounds (256-bit).
Each round mixes the data with substitution (SubBytes — an S-box), permutation (ShiftRows, MixColumns), and the key (AddRoundKey). Many rounds of small mixing make the output look totally random.
DES — সংক্ষিপ্ত ইতিহাস
DES (Data Encryption Standard) ছিল ১৯৭৭ সাল থেকে US-এর standard। এটা block cipher: 64-bit block, 56-bit key, 16 round mixing (Feistel structure)। ১৯৯০-এর শেষে computer এত fast হলো যে \(2^{56}\) key brute force করা গেল — একটা special machine কয়েক দিনে DES ভেঙে দেয়। 3DES (Triple DES) নামে patch এলো — DES তিনবার আলাদা key দিয়ে চালানো — কিন্তু slow। তাই নতুন standard বাছা হলো।
AES — বর্তমান standard
AES (Advanced Encryption Standard), ২০০১ সালে বাছাই (Rijndael algorithm), আজকের standard block cipher।
- Block size: সবসময় 128 bit।
- Key size: 128, 192, বা 256 bit।
- Round: 10 round (128-bit key), 12 round (192-bit), 14 round (256-bit)।
প্রতিটা round-এ data মেশানো হয় substitution (SubBytes — একটা S-box), permutation (ShiftRows, MixColumns) আর key (AddRoundKey) দিয়ে। অনেক round-এর ছোট ছোট mixing মিলে output একদম random-এর মতো দেখায়।
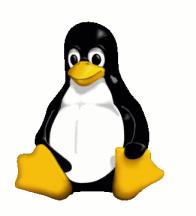
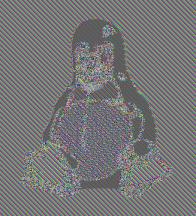
Modes of operation: ECB vs CBC
A block cipher only knows how to encrypt one block. A mode of operation says how to handle many blocks.
- ECB (Electronic Codebook) — encrypt each block separately: \(C_i = E_K(P_i)\). Problem: the same plaintext block always gives the same ciphertext block. Patterns in the data stay visible in the ciphertext.
- CBC (Cipher Block Chaining) — XOR each plaintext block with the previous ciphertext block first: \(C_i = E_K(P_i \oplus C_{i-1})\), starting with a random IV (initialization vector). Now identical plaintext blocks give different ciphertext blocks, so patterns disappear.
Mode of operation: ECB vs CBC
Block cipher শুধু একটা block encrypt করতে জানে। অনেক block কীভাবে সামলাবে সেটা বলে mode of operation।
- ECB (Electronic Codebook) — প্রতিটা block আলাদা encrypt: \(C_i = E_K(P_i)\)। সমস্যা: একই plaintext block সবসময় একই ciphertext block দেয়। Data-র pattern ciphertext-এও দেখা যায়।
- CBC (Cipher Block Chaining) — প্রতিটা plaintext block-কে আগের ciphertext block-এর সাথে আগে XOR করা হয়: \(C_i = E_K(P_i \oplus C_{i-1})\), শুরুটা হয় random IV (initialization vector) দিয়ে। এখন একই plaintext block আলাদা ciphertext দেয়, তাই pattern হারিয়ে যায়।
The key distribution problem
Symmetric encryption has one big weakness: both sides must already share the secret key. How do you send the key safely? If you send it over the network, an attacker may grab it. Meeting in person does not scale.
Also, keys grow fast. If \(n\) people all want private pairwise channels, each pair needs its own key:
Key distribution problem
Symmetric encryption-এর একটা বড় দুর্বলতা: দুই পক্ষের কাছেই আগে থেকে secret key থাকতে হবে। Key নিরাপদে পাঠাবে কীভাবে? Network দিয়ে পাঠালে attacker ধরে ফেলতে পারে। সবার সাথে সামনাসামনি দেখা করাও সম্ভব না।
তাছাড়া key-র সংখ্যা দ্রুত বাড়ে। \(n\) জন মানুষ সবাই সবার সাথে private channel চাইলে প্রতিটা pair-এর আলাদা key লাগে:
- Compression stops working after encryption. Compression works by finding repeated patterns (redundancy) in the data. Good ciphertext looks completely random — high entropy, no patterns. So if you encrypt first, the compressor finds almost nothing to squeeze, and the file barely shrinks.
- Compression before encryption helps security. Removing redundancy also removes the patterns (like letter frequencies) that an attacker could use for cryptanalysis. Less pattern in the plaintext means less for the attacker to exploit.
- Encryption-এর পরে compression কাজ করে না। Compression কাজ করে data-র ভেতরের repeated pattern (redundancy) খুঁজে। ভালো ciphertext একদম random দেখায় — high entropy, কোনো pattern নেই। তাই আগে encrypt করলে compressor চাপ দেওয়ার মতো প্রায় কিছুই পায় না, file প্রায় ছোটই হয় না।
- Encryption-এর আগে compression security-তেও সাহায্য করে। Redundancy সরালে সেই pattern-গুলোও (যেমন letter frequency) চলে যায়, যা attacker cryptanalysis-এ কাজে লাগাতে পারত। Plaintext-এ pattern কম মানে attacker-এর হাতে সুযোগও কম।
3. Asymmetric Encryption (RSA, Diffie-Hellman)3. Asymmetric Encryption (RSA, Diffie-Hellman)
The public/private key idea
In asymmetric encryption (also called public-key cryptography), every person has two keys:
- Public key — shared with everyone. Used to encrypt messages sent to you.
- Private key — kept secret. Used to decrypt messages you receive.
Mailbox analogy: your public key is like the slot of your mailbox. Anyone can drop a letter in (encrypt). But only you have the key to open the box and read the letters (decrypt with the private key).
The magic: the two keys are mathematically linked, but knowing the public key does not let you compute the private key (in a practical amount of time). This kills the key distribution problem — you never need to share a secret in advance.
Public/private key idea
Asymmetric encryption-এ (আরেক নাম public-key cryptography) প্রত্যেক মানুষের দুইটা key থাকে:
- Public key — সবাইকে দেওয়া হয়। তোমাকে পাঠানো message encrypt করতে ব্যবহার হয়।
- Private key — গোপন রাখা হয়। তোমার কাছে আসা message decrypt করতে ব্যবহার হয়।
Mailbox analogy: তোমার public key হলো তোমার mailbox-এর ফাঁক। যে কেউ চিঠি ফেলতে পারে (encrypt)। কিন্তু বাক্স খুলে চিঠি পড়ার চাবি (private key) শুধু তোমার কাছে।
Magic-টা হলো: দুই key math দিয়ে জোড়া, কিন্তু public key জানলেও private key বের করা যায় না (বাস্তব সময়ের মধ্যে)। এতে key distribution problem শেষ — আগে থেকে কোনো secret share করা লাগে না।
RSA — how it works
RSA (Rivest–Shamir–Adleman, 1977) is the most famous asymmetric algorithm. Its safety comes from one hard math fact: multiplying two big primes is easy, but factoring the product back into the primes is extremely hard.
Key generation steps (memorize this order):
- Choose two primes \(p\) and \(q\).
- Compute \(n = p \times q\). This \(n\) is the modulus.
- Compute Euler's totient: \(\varphi(n) = (p-1)(q-1)\).
- Choose public exponent \(e\) with \(1 < e < \varphi(n)\) and \(\gcd(e, \varphi(n)) = 1\).
- Find private exponent \(d\) such that \(e \times d \equiv 1 \pmod{\varphi(n)}\).
Public key = \((e, n)\). Private key = \((d, n)\). Then:
RSA — কীভাবে কাজ করে
RSA (Rivest–Shamir–Adleman, 1977) সবচেয়ে বিখ্যাত asymmetric algorithm। এর নিরাপত্তা একটা কঠিন math fact-এর উপর: দুইটা বড় prime গুণ করা সহজ, কিন্তু গুণফলকে factor করে prime দুটো ফেরত পাওয়া ভীষণ কঠিন।
Key generation-এর step (এই order মুখস্থ রাখো):
- দুইটা prime \(p\) আর \(q\) নাও।
- \(n = p \times q\) বের করো। এই \(n\) হলো modulus।
- Euler's totient বের করো: \(\varphi(n) = (p-1)(q-1)\)।
- Public exponent \(e\) নাও যেন \(1 < e < \varphi(n)\) আর \(\gcd(e, \varphi(n)) = 1\) হয়।
- Private exponent \(d\) বের করো যেন \(e \times d \equiv 1 \pmod{\varphi(n)}\) হয়।
Public key = \((e, n)\)। Private key = \((d, n)\)। তারপর:
- Compute \(n\): \(n = p \times q = 3 \times 11 = 33\).
- Compute \(\varphi(n)\): \(\varphi(n) = (3-1)(11-1) = 2 \times 10 = 20\).
- Choose \(e\): pick \(e = 3\). Check: \(\gcd(3, 20) = 1\). OK.
- Find \(d\): need \(3d \equiv 1 \pmod{20}\). Try: \(3 \times 7 = 21 = 20 + 1\). So \(d = 7\).
- Keys: public key \((e, n) = (3, 33)\), private key \((d, n) = (7, 33)\).
- Encrypt \(M = 4\): \(C = 4^3 \bmod 33 = 64 \bmod 33 = 31\).
- Decrypt \(C = 31\): \(M = 31^7 \bmod 33\). Shortcut: \(31 \equiv -2 \pmod{33}\), so \(31^7 \equiv (-2)^7 = -128 \pmod{33}\). Now \(-128 + 132 = 4\) (since \(132 = 4 \times 33\)). So \(M = 4\). ✓ We got the original message back.
- \(n\) বের করি: \(n = p \times q = 3 \times 11 = 33\)।
- \(\varphi(n)\) বের করি: \(\varphi(n) = (3-1)(11-1) = 2 \times 10 = 20\)।
- \(e\) বাছাই: \(e = 3\) নিই। Check: \(\gcd(3, 20) = 1\)। ঠিক আছে।
- \(d\) বের করি: দরকার \(3d \equiv 1 \pmod{20}\)। Try করি: \(3 \times 7 = 21 = 20 + 1\)। তাই \(d = 7\)।
- Key: public key \((e, n) = (3, 33)\), private key \((d, n) = (7, 33)\)।
- \(M = 4\) encrypt: \(C = 4^3 \bmod 33 = 64 \bmod 33 = 31\)।
- \(C = 31\) decrypt: \(M = 31^7 \bmod 33\)। Shortcut: \(31 \equiv -2 \pmod{33}\), তাই \(31^7 \equiv (-2)^7 = -128 \pmod{33}\)। এখন \(-128 + 132 = 4\) (কারণ \(132 = 4 \times 33\))। তাই \(M = 4\)। ✓ আসল message ফেরত পেলাম।
Diffie-Hellman key exchange
Diffie-Hellman (DH) solves a different problem: two people build a shared secret over a public channel, without ever sending the secret itself. It is used to agree on a symmetric key.
Setup: everyone agrees on a public prime \(p\) and a base \(g\). Then:
- Alice picks secret \(a\), sends \(A = g^a \bmod p\).
- Bob picks secret \(b\), sends \(B = g^b \bmod p\).
- Alice computes \(S = B^a \bmod p\). Bob computes \(S = A^b \bmod p\).
- Both get the same \(S = g^{ab} \bmod p\) — the shared secret.
An eavesdropper sees \(p, g, A, B\) but cannot find \(a\) or \(b\) — that would need solving the discrete logarithm problem, which is very hard for big numbers.
Paint analogy: both start with the same public color. Each mixes in a private color and swaps the mixture. Each then adds their private color again. Both end with the same final color, but an observer who saw only the mixtures cannot un-mix the paint.
Diffie-Hellman key exchange
Diffie-Hellman (DH) অন্য একটা সমস্যা solve করে: দুইজন মানুষ public channel-এর উপর দিয়েই একটা shared secret বানায়, secret-টা কখনো না পাঠিয়েই। এটা দিয়ে symmetric key ঠিক করা হয়।
Setup: সবাই একটা public prime \(p\) আর base \(g\) ঠিক করে। তারপর:
- Alice secret \(a\) নেয়, পাঠায় \(A = g^a \bmod p\)।
- Bob secret \(b\) নেয়, পাঠায় \(B = g^b \bmod p\)।
- Alice বের করে \(S = B^a \bmod p\)। Bob বের করে \(S = A^b \bmod p\)।
- দুজনেই পায় একই \(S = g^{ab} \bmod p\) — এটাই shared secret।
আড়িপাতা কেউ \(p, g, A, B\) দেখে, কিন্তু \(a\) বা \(b\) বের করতে পারে না — তার জন্য discrete logarithm problem solve করতে হবে, যা বড় সংখ্যায় ভীষণ কঠিন।
Paint analogy: দুজনেই একই public রং দিয়ে শুরু করে। প্রত্যেকে নিজের private রং মিশিয়ে মিশ্রণটা বিনিময় করে। তারপর আবার নিজের private রং মেশায়। দুজনের শেষ রং একই হয়, কিন্তু মাঝখানে শুধু মিশ্রণ দেখা observer রং আলাদা করতে পারে না।
- Alice computes A: \(5^2 = 25 \equiv 2 \pmod{23}\); \(5^4 \equiv 2^2 = 4\); \(5^6 = 5^4 \times 5^2 \equiv 4 \times 2 = 8\). So \(A = 8\).
- Bob computes B: \(5^8 \equiv 4^2 = 16\); \(5^{15} = 5^8 \times 5^4 \times 5^2 \times 5^1 \equiv 16 \times 4 \times 2 \times 5\). Step by step: \(16 \times 4 = 64 \equiv 64 - 46 = 18\); \(18 \times 2 = 36 \equiv 13\); \(13 \times 5 = 65 \equiv 65 - 46 = 19\). So \(B = 19\).
- Alice's secret: \(S = B^a = 19^6 \bmod 23\). Trick: \(19 \equiv -4 \pmod{23}\), so \(19^6 \equiv (-4)^6 = 4096\). And \(4096 = 178 \times 23 + 2\), so \(S = 2\).
- Bob's secret: \(S = A^b = 8^{15} \bmod 23\). Note \(8 = 2^3\), so \(8^{15} = 2^{45}\). Since \(2^{11} = 2048 = 89 \times 23 + 1 \equiv 1\), we get \(2^{45} = (2^{11})^4 \times 2 \equiv 1 \times 2 = 2\). So \(S = 2\).
- Alice-এর A: \(5^2 = 25 \equiv 2 \pmod{23}\); \(5^4 \equiv 2^2 = 4\); \(5^6 = 5^4 \times 5^2 \equiv 4 \times 2 = 8\)। তাই \(A = 8\)।
- Bob-এর B: \(5^8 \equiv 4^2 = 16\); \(5^{15} = 5^8 \times 5^4 \times 5^2 \times 5^1 \equiv 16 \times 4 \times 2 \times 5\)। ধাপে ধাপে: \(16 \times 4 = 64 \equiv 64 - 46 = 18\); \(18 \times 2 = 36 \equiv 13\); \(13 \times 5 = 65 \equiv 65 - 46 = 19\)। তাই \(B = 19\)।
- Alice-এর secret: \(S = B^a = 19^6 \bmod 23\)। Trick: \(19 \equiv -4 \pmod{23}\), তাই \(19^6 \equiv (-4)^6 = 4096\)। আর \(4096 = 178 \times 23 + 2\), তাই \(S = 2\)।
- Bob-এর secret: \(S = A^b = 8^{15} \bmod 23\)। লক্ষ করো \(8 = 2^3\), তাই \(8^{15} = 2^{45}\)। যেহেতু \(2^{11} = 2048 = 89 \times 23 + 1 \equiv 1\), পাই \(2^{45} = (2^{11})^4 \times 2 \equiv 1 \times 2 = 2\)। তাই \(S = 2\)।
Symmetric vs Asymmetric — comparison
Symmetric vs Asymmetric — তুলনা
| FeatureFeature | Symmetric | Asymmetric |
|---|---|---|
| Keys usedযে key লাগে | One shared secret keyএকটা shared secret key | Key pair: public + privateKey pair: public + private |
| Speedগতি | Very fastখুব fast | Slow (100–1000× slower)Slow (100–1000 গুণ slow) |
| Keys for n peoplen জনের জন্য key | \( \frac{n(n-1)}{2} \) | \( 2n \) |
| Key distributionKey distribution | Hard — must share secret firstকঠিন — আগে secret share করতে হয় | Easy — publish the public keyসহজ — public key ছড়িয়ে দিলেই হয় |
| Typical useসাধারণ ব্যবহার | Bulk data encryptionবড় data encryption | Key exchange, digital signaturesKey exchange, digital signature |
| Examplesউদাহরণ | AES, DES, 3DES, ChaCha20 | RSA, Diffie-Hellman, ECC, ElGamal |
Hybrid encryption — best of both
Real systems use both together. Asymmetric crypto is slow, so we do not encrypt whole files with RSA. Instead:
- Generate a random symmetric session key.
- Encrypt the big data with the session key (fast AES).
- Encrypt only the small session key with the receiver's public key (RSA).
- Send both. The receiver unlocks the session key with the private key, then decrypts the data.
This is exactly how HTTPS/TLS, PGP email, and most secure systems work.
Hybrid encryption — দুটোর সেরা মিলে
বাস্তব system দুটোই একসাথে ব্যবহার করে। Asymmetric crypto slow, তাই পুরো file RSA দিয়ে encrypt করা হয় না। বরং:
- একটা random symmetric session key বানাও।
- বড় data-টা session key দিয়ে encrypt করো (fast AES)।
- শুধু ছোট session key-টা receiver-এর public key দিয়ে encrypt করো (RSA)।
- দুটোই পাঠাও। Receiver private key দিয়ে session key খোলে, তারপর data decrypt করে।
HTTPS/TLS, PGP email — বেশিরভাগ secure system ঠিক এভাবেই কাজ করে।
4. Hashing & Digital Signatures4. Hashing & Digital Signatures
What is a hash function?
A cryptographic hash function takes any input (a message, a file of any size) and produces a fixed-size output called the hash or digest. Example: SHA-256("hello") is always the same 256-bit value.
Key properties:
- Deterministic — same input always gives the same hash.
- Fast — quick to compute for any input.
- One-way (preimage resistance) — given a hash, you cannot find the input. There is no "decrypt" for a hash.
- Collision resistance — it is practically impossible to find two different inputs with the same hash.
- Avalanche effect — change one bit of the input and about half of the output bits flip. "hello" and "hellp" give totally different hashes.
Hash function কী?
Cryptographic hash function যেকোনো input (যেকোনো সাইজের message বা file) নিয়ে একটা নির্দিষ্ট সাইজের output দেয়, যাকে বলে hash বা digest। যেমন: SHA-256("hello") সবসময় একই 256-bit value।
মূল property:
- Deterministic — একই input সবসময় একই hash দেয়।
- Fast — যেকোনো input-এ দ্রুত হিসাব হয়।
- One-way (preimage resistance) — hash দেখে input বের করা যায় না। Hash-এর কোনো "decrypt" নেই।
- Collision resistance — দুইটা আলাদা input-এর একই hash পাওয়া কার্যত অসম্ভব।
- Avalanche effect — input-এর এক bit বদলালে output-এর প্রায় অর্ধেক bit বদলে যায়। "hello" আর "hellp"-এর hash সম্পূর্ণ আলাদা।
Common hash functions
পরিচিত hash function গুলো
| Algorithm | Output sizeOutput size | Statusঅবস্থা |
|---|---|---|
| MD5 | 128 bit | Broken — collisions found; never use for securityBroken — collision পাওয়া গেছে; security-তে ব্যবহার নিষেধ |
| SHA-1 | 160 bit | Broken (2017 collision); deprecatedBroken (2017-এ collision); deprecated |
| SHA-256 (SHA-2 family) | 256 bit | Secure, widely used (TLS, Bitcoin)Secure, বহুল ব্যবহৃত (TLS, Bitcoin) |
| SHA-512 (SHA-2 family) | 512 bit | SecureSecure |
| SHA-3 (Keccak) | 224–512 bit | Secure, newest standard (2015)Secure, নতুনতম standard (2015) |
Password storage and salting
Servers must never store passwords as plaintext. They store the hash of the password. At login, the server hashes what you typed and compares hashes.
But attackers precompute hashes of common passwords (rainbow tables). The fix is a salt: a random value added to each password before hashing.
stored = hash(salt + password) // salt is random, stored next to the hash- Same password + different salts → different hashes. Precomputed tables become useless.
- Two users with the same password get different stored hashes.
- Real systems also use slow hashes (bcrypt, scrypt, Argon2) so brute forcing each guess is expensive.
Password রাখা আর salting
Server কখনোই password plaintext-এ রাখবে না। রাখে password-এর hash। Login-এর সময় server তোমার টাইপ করা password hash করে hash-এ hash-এ মেলায়।
কিন্তু attacker-রা common password-এর hash আগেই বানিয়ে রাখে (rainbow table)। সমাধান হলো salt: প্রতিটা password-এর সাথে hash করার আগে একটা random value যোগ করা।
stored = hash(salt + password) // salt random, hash-এর পাশেই রাখা হয়- একই password + আলাদা salt → আলাদা hash। আগে বানানো table অকেজো হয়ে যায়।
- একই password-ওয়ালা দুই user-এর stored hash আলাদা হয়।
- বাস্তব system-এ slow hash-ও ব্যবহার হয় (bcrypt, scrypt, Argon2) যাতে প্রতিটা guess try করা ব্যয়বহুল হয়।
MAC — Message Authentication Code
A plain hash proves nothing about who sent the message — anyone can hash. A MAC mixes a shared secret key into the hash: \( \text{MAC} = H(K, M) \). Only someone who knows \(K\) can produce or verify the MAC. It gives integrity + authenticity between two parties who share a key. HMAC (e.g., HMAC-SHA256) is the standard construction.
MAC — Message Authentication Code
সাধারণ hash প্রমাণ করে না message কে পাঠিয়েছে — hash তো যে কেউ করতে পারে। MAC hash-এর সাথে একটা shared secret key মেশায়: \( \text{MAC} = H(K, M) \)। শুধু \(K\) জানা মানুষই MAC বানাতে বা verify করতে পারে। এটা shared key-ওয়ালা দুই পক্ষের মধ্যে integrity + authenticity দেয়। Standard construction হলো HMAC (যেমন HMAC-SHA256)।
Digital signatures
A digital signature is like a handwritten signature, but unforgeable and tied to the exact document. The trick: use the asymmetric keys in the opposite direction from encryption.
- Sign: the sender hashes the message, then encrypts the hash with their private key. That encrypted hash is the signature.
- Verify: the receiver decrypts the signature with the sender's public key to get hash₁, hashes the received message to get hash₂, and checks hash₁ = hash₂.
If they match: the message came from the private-key owner (authenticity), was not changed (integrity), and the sender cannot deny sending it (non-repudiation).
Signature vs encryption — direction matters:
- Encryption for secrecy: encrypt with receiver's public key → decrypt with receiver's private key.
- Signature for proof: sign with sender's private key → verify with sender's public key.
Digital signature
Digital signature হাতের signature-এর মতো, কিন্তু নকল করা যায় না আর নির্দিষ্ট document-এর সাথে বাঁধা। Trick-টা হলো: asymmetric key-গুলো encryption-এর উল্টো দিকে ব্যবহার করা।
- Sign: sender message-টা hash করে, তারপর hash-টা নিজের private key দিয়ে encrypt করে। এই encrypted hash-ই signature।
- Verify: receiver sender-এর public key দিয়ে signature decrypt করে hash₁ পায়, পাওয়া message hash করে hash₂ পায়, তারপর check করে hash₁ = hash₂ কি না।
মিললে: message private-key-র মালিকের কাছ থেকেই এসেছে (authenticity), বদলানো হয়নি (integrity), আর sender অস্বীকার করতে পারবে না (non-repudiation)।
Signature vs encryption — দিকটাই আসল:
- গোপনীয়তার জন্য encryption: receiver-এর public key দিয়ে encrypt → receiver-এর private key দিয়ে decrypt।
- প্রমাণের জন্য signature: sender-এর private key দিয়ে sign → sender-এর public key দিয়ে verify।
- Sign: \(S = H^d \bmod n = 5^7 \bmod 33\). Compute: \(5^2 = 25\), \(5^4 = 625 \bmod 33 = 625 - 594 = 31 \equiv -2\), so \(5^7 = 5^4 \times 5^2 \times 5 \equiv (-2)(25)(5) = -250 \bmod 33\). \(-250 + 264 = 14\). Signature \(S = 14\).
- Verify: \(S^e \bmod n = 14^3 \bmod 33 = 2744 \bmod 33\). \(33 \times 83 = 2739\), so result = 5 = \(H\). ✓ Signature is valid.
- Sign: \(S = H^d \bmod n = 5^7 \bmod 33\)। হিসাব: \(5^2 = 25\), \(5^4 = 625 \bmod 33 = 625 - 594 = 31 \equiv -2\), তাই \(5^7 = 5^4 \times 5^2 \times 5 \equiv (-2)(25)(5) = -250 \bmod 33\)। \(-250 + 264 = 14\)। Signature \(S = 14\)।
- Verify: \(S^e \bmod n = 14^3 \bmod 33 = 2744 \bmod 33\)। \(33 \times 83 = 2739\), তাই result = 5 = \(H\)। ✓ Signature valid।
Certificates and the CA chain (briefly)
One question remains: how do you know a public key really belongs to "bob.com" and not to an attacker? A digital certificate answers this. It is a document saying "this public key belongs to bob.com", signed by a trusted third party called a Certificate Authority (CA).
- Your browser ships with a list of trusted root CAs.
- A root CA signs an intermediate CA's certificate; the intermediate signs the website's certificate. This is the chain of trust.
- The browser verifies each signature up the chain to a trusted root. If any link fails, you see a certificate warning.
Certificate আর CA chain (সংক্ষেপে)
একটা প্রশ্ন থেকে যায়: কীভাবে বুঝবে একটা public key সত্যিই "bob.com"-এর, কোনো attacker-এর না? উত্তর দেয় digital certificate। এটা একটা document যেখানে লেখা "এই public key bob.com-এর", আর সেটায় sign করে একটা বিশ্বস্ত তৃতীয় পক্ষ — Certificate Authority (CA)।
- তোমার browser-এ বিশ্বস্ত root CA-দের list আগে থেকেই দেওয়া থাকে।
- Root CA sign করে intermediate CA-র certificate-এ; intermediate sign করে website-এর certificate-এ। এটাই chain of trust।
- Browser chain ধরে প্রতিটা signature verify করে trusted root পর্যন্ত যায়। কোনো link fail করলে certificate warning দেখায়।
5. Authentication & Access Control5. Authentication & Access Control
Authentication — proving who you are
Authentication means proving your identity to a system. There are three classic factors:
- Something you know — password, PIN, security question.
- Something you have — phone (OTP app/SMS), smart card, hardware token.
- Something you are — biometrics: fingerprint, face, iris, voice.
Two-factor authentication (2FA) combines two different factors — for example password (know) + OTP on phone (have). Even if the password leaks, the attacker still cannot log in. Password + security question is NOT 2FA — both are "something you know".
Password best practice: long passphrases beat short complex ones; unique password per site; use a password manager; server side, store salted slow hashes (previous section).
Biometrics: convenient, hard to forge, but they have false accepts/rejects, and you cannot change your fingerprint if the template leaks. Best used as one factor among several.
Authentication — তুমি কে, তা প্রমাণ
Authentication মানে system-এর কাছে নিজের পরিচয় প্রমাণ করা। তিনটা classic factor আছে:
- Something you know — password, PIN, security question।
- Something you have — phone (OTP app/SMS), smart card, hardware token।
- Something you are — biometrics: fingerprint, face, iris, voice।
Two-factor authentication (2FA) দুইটা আলাদা factor মেলায় — যেমন password (know) + phone-এ OTP (have)। Password ফাঁস হলেও attacker ঢুকতে পারে না। Password + security question কিন্তু 2FA না — দুটোই "something you know"।
Password best practice: ছোট জটিল password-এর চেয়ে লম্বা passphrase ভালো; প্রতিটা site-এ আলাদা password; password manager ব্যবহার করো; server-এ salted slow hash রাখো (আগের section)।
Biometrics: সুবিধাজনক, নকল করা কঠিন, কিন্তু false accept/reject হয়, আর template ফাঁস হলে fingerprint তো বদলানো যায় না। কয়েকটা factor-এর একটা হিসেবে ব্যবহারই সেরা।
Authentication vs Authorization
- Authentication — who are you? (login step)
- Authorization — what are you allowed to do? (permission step, after login)
Example: you log into the university portal (authentication). Then a student can view grades but only a teacher can edit them (authorization). Authentication always happens first.
Authentication vs Authorization
- Authentication — তুমি কে? (login step)
- Authorization — তোমার কী কী করার অনুমতি আছে? (login-এর পরের permission step)
যেমন: university portal-এ login করলে (authentication)। তারপর student শুধু grade দেখতে পারে কিন্তু teacher-ই edit করতে পারে (authorization)। Authentication সবসময় আগে হয়।
Access control models: DAC, MAC, RBAC
Access control model: DAC, MAC, RBAC
| Model | Who decides access?Access কে ঠিক করে? | Exampleউদাহরণ |
|---|---|---|
| DAC (Discretionary)(Discretionary) |
The owner of the resource decides who gets access.Resource-এর owner ঠিক করে কে access পাবে। | Linux file permissions (chmod), sharing a Google Doc with a friend.Linux file permission (chmod), বন্ধুর সাথে Google Doc share করা। |
| MAC (Mandatory)(Mandatory) |
A central policy with security labels decides; owners cannot override.Security label-ওয়ালা central policy ঠিক করে; owner-ও বদলাতে পারে না। | Military systems: Top Secret / Secret / Confidential clearance levels, SELinux.Military system: Top Secret / Secret / Confidential clearance level, SELinux। |
| RBAC (Role-Based)(Role-Based) |
Permissions attach to roles; users get roles.Permission থাকে role-এর সাথে; user-কে role দেওয়া হয়। | Hospital software: "doctor" role can prescribe, "receptionist" role can book appointments.Hospital software: "doctor" role prescribe করতে পারে, "receptionist" role appointment দিতে পারে। |
ACL vs Capabilities
Think of the access control matrix: rows = users, columns = resources. Two ways to store it:
- ACL (Access Control List) — stored per resource (column): "file report.txt: Alice can read+write, Bob can read." Easy question: "who can access this file?"
- Capability list — stored per user (row): "Alice holds tickets for: report.txt (rw), photo.png (r)." Easy question: "what can Alice access?" A capability is like a movie ticket — holding it is the permission.
Principle of least privilege
Give every user and every program the minimum access needed to do its job — nothing more. A web server does not need to read user home directories; an intern does not need admin rights. If something is compromised, the damage stays small. Related idea: defense in depth — use several layers of protection so one failure does not sink the whole system.
ACL vs Capabilities
Access control matrix ভাবো: row = user, column = resource। এটা রাখার দুইটা উপায়:
- ACL (Access Control List) — প্রতি resource-এ রাখা হয় (column): "file report.txt: Alice read+write পারে, Bob read পারে।" সহজ প্রশ্ন: "এই file-এ কে কে access পায়?"
- Capability list — প্রতি user-এ রাখা হয় (row): "Alice-এর ticket আছে: report.txt (rw), photo.png (r)।" সহজ প্রশ্ন: "Alice কী কী access পায়?" Capability হলো cinema ticket-এর মতো — ticket থাকাটাই permission।
Principle of least privilege
প্রতিটা user আর program-কে কাজের জন্য ন্যূনতম যতটুকু access দরকার ততটুকুই দাও — তার বেশি না। Web server-এর user-দের home directory পড়ার দরকার নেই; intern-এর admin right দরকার নেই। কিছু compromise হলেও ক্ষতি ছোট থাকে। কাছাকাছি idea: defense in depth — কয়েক স্তরের protection রাখো, যেন একটা fail করলেই পুরো system না ডোবে।
chmod 640 report.txt means: owner can read+write (6 = rw-), group can read (4 = r--), others get nothing (0 = ---). The owner set this — that is why Linux permissions are DAC.chmod 640 report.txt মানে: owner read+write পারে (6 = rw-), group read পারে (4 = r--), others কিছুই না (0 = ---)। Owner নিজেই এটা set করেছে — এজন্যই Linux permission হলো DAC।6. Common Network & Security Concepts6. Common Network & Security Concepts
Malware types
Malware = malicious software. Know the difference between the main types — exams love this table.
Malware-এর ধরন
Malware = malicious software। মূল ধরনগুলোর পার্থক্য জানো — exam-এ এই table খুব আসে।
| Typeধরন | What it doesকী করে | Key pointমূল কথা |
|---|---|---|
| Virus | Attaches itself to a program or file; runs when the host runs.কোনো program বা file-এর সাথে জুড়ে যায়; host চললে সে-ও চলে। | Needs a host file and user action to spread.ছড়াতে host file আর user-এর action লাগে। |
| Worm | Spreads by itself over the network, machine to machine.Network দিয়ে নিজে নিজেই এক machine থেকে আরেক machine-এ ছড়ায়। | Self-replicating; no host file needed.Self-replicating; host file লাগে না। |
| Trojan | Pretends to be useful software; does harm secretly after you install it.দরকারি software সেজে থাকে; install করার পর গোপনে ক্ষতি করে। | Tricks the user; does not self-replicate.User-কে ধোঁকা দেয়; নিজে replicate করে না। |
| Ransomware | Encrypts your files and demands money for the key.তোমার file encrypt করে key-র জন্য টাকা দাবি করে। | Best defense: offline backups.সেরা defense: offline backup। |
| Spyware / Keylogger | Secretly records your activity or keystrokes.গোপনে তোমার activity বা keystroke record করে। | Breaks confidentiality.Confidentiality ভাঙে। |
Phishing and social engineering
Social engineering attacks the human, not the machine — tricking people into giving up secrets. Phishing is the most common form: a fake email or website that looks real (e.g., "your bank" asking you to "verify" your password). Spear phishing targets a specific person with personalized details.
Defense: check the real sender address and URL, never enter credentials from an email link, enable 2FA (so a stolen password alone fails), and train users. Organizations run awareness training because no firewall can stop a user who is tricked.
DoS and DDoS
A Denial of Service (DoS) attack floods a server with so many requests (or such heavy requests) that real users cannot be served — it attacks availability. A DDoS (Distributed DoS) does this from thousands of hijacked machines (a botnet) at once, which is much harder to block because there is no single source to filter.
Defense: rate limiting, traffic filtering, load balancers, and large CDN/scrubbing services that absorb and clean the traffic.
Man-in-the-middle (MITM)
An attacker secretly sits between two parties, relaying (and possibly changing) their messages. Both sides think they talk directly. Example risk: open public Wi-Fi where the attacker controls the access point.
Defense: authenticated encryption — HTTPS/TLS with certificates. The certificate check is exactly what stops an attacker from pretending to be the server. This is also why plain Diffie-Hellman needs signatures/certificates.
Phishing আর social engineering
Social engineering machine-কে না, মানুষকে attack করে — মানুষ ভুলিয়ে secret আদায় করা। Phishing এর সবচেয়ে common রূপ: আসলের মতো দেখতে নকল email বা website (যেমন "তোমার bank" বলছে password "verify" করতে)। Spear phishing নির্দিষ্ট একজনকে personalized তথ্য দিয়ে target করে।
Defense: আসল sender address আর URL check করো, email-এর link থেকে কখনো credential দিও না, 2FA চালু রাখো (password চুরি হলেও কাজ হবে না), আর user-দের train করো। Organization-গুলো awareness training করায়, কারণ ধোঁকা খাওয়া user-কে কোনো firewall আটকাতে পারে না।
DoS আর DDoS
Denial of Service (DoS) attack-এ server-কে এত request (বা এত ভারী request) পাঠানো হয় যে আসল user-রা service পায় না — এটা availability-র উপর attack। DDoS (Distributed DoS) এটাই করে হাজার হাজার hijack করা machine (একটা botnet) থেকে একসাথে — এটা আটকানো অনেক কঠিন, কারণ filter করার মতো একক source নেই।
Defense: rate limiting, traffic filtering, load balancer, আর বড় CDN/scrubbing service যারা traffic শুষে নিয়ে পরিষ্কার করে।
Man-in-the-middle (MITM)
Attacker গোপনে দুই পক্ষের মাঝে বসে message relay করে (চাইলে বদলেও দেয়)। দুই পক্ষই ভাবে তারা সরাসরি কথা বলছে। ঝুঁকির উদাহরণ: open public Wi-Fi, যেখানে attacker-ই access point চালায়।
Defense: authenticated encryption — certificate-সহ HTTPS/TLS। Certificate check-টাই attacker-কে server সাজতে দেয় না। এজন্যই সাধারণ Diffie-Hellman-এর সাথে signature/certificate লাগে।
DHCP starvation
Remember: a DHCP server hands out IP addresses to devices that join a network, and it only has a limited pool of addresses. In a DHCP starvation attack, the attacker sends a flood of DHCP DISCOVER requests, each with a different spoofed (fake) MAC address. The server thinks many new devices are joining and reserves an IP for each fake one. Soon the whole address pool is empty — real clients ask for an IP and get nothing, so they cannot use the network. It is a DoS attack on the DHCP service (an attack on availability).
It gets worse: the attacker often pairs this with a rogue DHCP server. Once the real server is starved, the attacker's fake server answers the clients instead — handing out attacker-controlled settings like a malicious gateway or DNS server. Now the attacker sits in the middle of everyone's traffic (a MITM setup).
Defense: at the switch level. DHCP snooping lets the switch mark which ports may carry DHCP server replies (trusted ports) and drops fake server replies from other ports. Port security limits how many MAC addresses one switch port may use, so one port cannot pretend to be thousands of devices.
DHCP starvation
মনে করো: DHCP server network-এ যোগ দেওয়া device-দের IP address দেয়, আর তার address-এর pool সীমিত। DHCP starvation attack-এ attacker অনেকগুলো DHCP DISCOVER request পাঠায়, প্রতিটাতে আলাদা spoofed (নকল) MAC address। Server ভাবে অনেক নতুন device আসছে, আর প্রতিটা নকল device-এর জন্য একটা করে IP আটকে রাখে। কিছুক্ষণেই পুরো address pool খালি — আসল client IP চেয়ে কিছুই পায় না, network ব্যবহার করতে পারে না। এটা DHCP service-এর উপর একটা DoS attack (availability-র উপর attack)।
আরো খারাপ দিক: attacker প্রায়ই এর সাথে একটা rogue DHCP server জুড়ে দেয়। আসল server starve হয়ে গেলে attacker-এর নকল server-ই client-দের উত্তর দেয় — attacker-এর নিয়ন্ত্রণে থাকা setting দেয়, যেমন malicious gateway বা DNS server। এখন attacker সবার traffic-এর মাঝখানে বসে (একটা MITM setup)।
Defense: switch level-এ। DHCP snooping দিয়ে switch ঠিক করে কোন port-এ DHCP server-এর reply আসতে পারবে (trusted port), আর অন্য port থেকে আসা নকল server reply ফেলে দেয়। Port security একটা switch port-এ কয়টা MAC address চলবে তা সীমিত করে, তাই এক port হাজার হাজার device সাজতে পারে না।
SQL injection
A web form asks for a username. The server builds a query by gluing strings:
query = "SELECT * FROM users WHERE name = '" + input + "'";If the input contains SQL syntax (like a quote character), the data becomes part of the command — the attacker's text is executed as SQL. This can leak or destroy the whole database. It breaks the rule: never mix code and data.
Why parameterized queries fix it: a parameterized (prepared) statement sends the SQL command and the data separately:
stmt = prepare("SELECT * FROM users WHERE name = ?");
stmt.bind(1, input);   // input is ALWAYS treated as pure data
The database compiles the query structure first, then plugs the input in as a pure value. Whatever the user types, it can never change the query's structure. Extra layers: input validation and least-privilege database accounts.
XSS — Cross-Site Scripting
XSS is the same "code mixed with data" mistake, but in the browser. A site shows user-submitted content (like a comment) without cleaning it. If the comment contains a script tag, other visitors' browsers run it — it can steal their cookies/sessions.
Defense: escape/encode output (so < is shown as text, not parsed as HTML), validate input, and set a Content Security Policy (CSP). Frameworks like React escape output by default.
SQL injection
একটা web form username চায়। Server string জোড়া দিয়ে query বানায়:
query = "SELECT * FROM users WHERE name = '" + input + "'";Input-এ SQL syntax (যেমন quote character) থাকলে data ঢুকে যায় command-এর ভেতরে — attacker-এর লেখা SQL হিসেবে চলে যায়। এতে পুরো database ফাঁস বা নষ্ট হতে পারে। এটা একটা নিয়ম ভাঙে: code আর data কখনো মেশাবে না।
Parameterized query কেন এটা ঠিক করে: parameterized (prepared) statement SQL command আর data আলাদা করে পাঠায়:
stmt = prepare("SELECT * FROM users WHERE name = ?");
stmt.bind(1, input);   // input সবসময় শুধুই data হিসেবে যায়
Database আগে query-র structure compile করে, তারপর input-কে শুধু value হিসেবে বসায়। User যা-ই লিখুক, query-র structure বদলাতে পারবে না। বাড়তি স্তর: input validation আর least-privilege database account।
XSS — Cross-Site Scripting
XSS সেই একই "code-data মেশানো" ভুল, কিন্তু browser-এ। কোনো site user-এর দেওয়া content (যেমন comment) পরিষ্কার না করে দেখায়। Comment-এ script tag থাকলে অন্য visitor-দের browser সেটা চালিয়ে দেয় — তাদের cookie/session চুরি হতে পারে।
Defense: output escape/encode করো (যেন < text হিসেবে দেখায়, HTML হিসেবে parse না হয়), input validate করো, আর Content Security Policy (CSP) দাও। React-এর মতো framework by default output escape করে।
Firewalls
A firewall sits between networks and decides which traffic may pass, based on rules.
- Packet-filtering firewall — checks each packet alone: source/destination IP, port, protocol. Fast, simple, but has no memory of connections.
- Stateful firewall — remembers active connections; allows replies that belong to a connection you started, blocks unexpected packets. This is the common modern type.
- Application-layer firewall / WAF — understands the application protocol (e.g., HTTP) and can block things like SQL injection patterns.
IDS and IPS
- IDS (Intrusion Detection System) — watches traffic/logs and raises an alarm when it sees an attack. It does not block.
- IPS (Intrusion Prevention System) — sits inline and blocks the attack traffic automatically.
Detection styles: signature-based (matches known attack patterns; misses new attacks) vs anomaly-based (flags unusual behavior; can catch new attacks but gives false positives).
VPN
A VPN (Virtual Private Network) builds an encrypted tunnel between your device and a VPN server. All your traffic travels inside the tunnel, so people on the local network (like café Wi-Fi) see only encrypted data going to the VPN server. Companies use VPNs so remote employees can reach the office network as if they were inside it.
SSL/TLS handshake (overview)
TLS (the modern name for SSL) is the protocol behind HTTPS. It combines almost everything in this chapter. Simplified handshake:
- Hello: client and server agree on TLS version and cipher suite; they exchange random values.
- Certificate: the server sends its certificate. The client verifies the CA chain — this authenticates the server.
- Key exchange: using Diffie-Hellman (or the server's RSA key), both sides derive a shared session key.
- Secure channel: all further data is encrypted with fast symmetric encryption (e.g., AES) plus integrity protection (MAC/AEAD).
So: certificates + signatures give authenticity, DH gives the shared key, AES gives speed — the hybrid model in action.
Firewall
Firewall network-গুলোর মাঝে বসে rule অনুযায়ী ঠিক করে কোন traffic যেতে পারবে।
- Packet-filtering firewall — প্রতিটা packet আলাদা করে দেখে: source/destination IP, port, protocol। Fast, simple, কিন্তু connection-এর কোনো স্মৃতি নেই।
- Stateful firewall — চালু connection মনে রাখে; তোমার শুরু করা connection-এর reply ঢুকতে দেয়, অপ্রত্যাশিত packet আটকায়। আজকের common ধরন এটাই।
- Application-layer firewall / WAF — application protocol (যেমন HTTP) বোঝে, SQL injection pattern-এর মতো জিনিসও আটকাতে পারে।
IDS আর IPS
- IDS (Intrusion Detection System) — traffic/log দেখে attack পেলে alarm বাজায়। Block করে না।
- IPS (Intrusion Prevention System) — traffic-এর পথে (inline) বসে attack নিজেই block করে।
Detection-এর ধরন: signature-based (জানা attack pattern মেলায়; নতুন attack ধরতে পারে না) vs anomaly-based (অস্বাভাবিক আচরণ ধরে; নতুন attack ধরতে পারে কিন্তু false positive দেয়)।
VPN
VPN (Virtual Private Network) তোমার device আর VPN server-এর মাঝে একটা encrypted tunnel বানায়। সব traffic tunnel-এর ভেতর দিয়ে যায়, তাই local network-এর লোকজন (যেমন café-র Wi-Fi) শুধু দেখে encrypted data VPN server-এ যাচ্ছে। Company-রা VPN ব্যবহার করে যেন remote employee-রা office network-এ ভেতরের মতোই ঢুকতে পারে।
SSL/TLS handshake (overview)
TLS (SSL-এর আধুনিক নাম) হলো HTTPS-এর পেছনের protocol। এই chapter-এর প্রায় সব কিছু এখানে মেলে। সরলীকৃত handshake:
- Hello: client আর server TLS version আর cipher suite ঠিক করে; random value বিনিময় করে।
- Certificate: server তার certificate পাঠায়। Client CA chain verify করে — এতে server authenticate হয়।
- Key exchange: Diffie-Hellman (বা server-এর RSA key) দিয়ে দুই পক্ষ একটা shared session key বানায়।
- Secure channel: এরপরের সব data fast symmetric encryption (যেমন AES) আর integrity protection (MAC/AEAD) দিয়ে যায়।
অর্থাৎ: certificate + signature দেয় authenticity, DH দেয় shared key, AES দেয় speed — hybrid model-এর বাস্তব রূপ।
Practice Questions (Admission Style)Practice Questions (Admission Style)
Show Answerউত্তর দেখুন
Show Answerউত্তর দেখুন
Show Answerউত্তর দেখুন
Show Answerউত্তর দেখুন
Show Answerউত্তর দেখুন
- F (5) → \( (5-3) \bmod 26 = 2 \) → C
- R (17) → \( (17-3) \bmod 26 = 14 \) → O
- P (15) → \( (15-3) \bmod 26 = 12 \) → M
- S (18) → P, X (23) → U, W (22) → T, H (7) → E, U (20) → R
- F (5) → \( (5-3) \bmod 26 = 2 \) → C
- R (17) → \( (17-3) \bmod 26 = 14 \) → O
- P (15) → \( (15-3) \bmod 26 = 12 \) → M
- S (18) → P, X (23) → U, W (22) → T, H (7) → E, U (20) → R
Show Answerউত্তর দেখুন
Show Answerউত্তর দেখুন
Show Answerউত্তর দেখুন
Show Answerউত্তর দেখুন
Show Answerউত্তর দেখুন
Show Answerউত্তর দেখুন
Show Answerউত্তর দেখুন
- \(n = 5 \times 11 = 55\); \(\varphi(n) = (5-1)(11-1) = 4 \times 10 = 40\).
- Need \(3d \equiv 1 \pmod{40}\). Try multiples: \(3 \times 27 = 81 = 2 \times 40 + 1\). So \(d = 27\).
- Encrypt: \(C = 7^3 \bmod 55 = 343 \bmod 55\). \(55 \times 6 = 330\), so \(C = 13\).
- Decrypt: \(M = 13^{27} \bmod 55\). By repeated squaring: \(13^2 = 169 \equiv 4\); \(13^4 \equiv 4^2 = 16\); \(13^8 \equiv 16^2 = 256 \equiv 36\); \(13^{16} \equiv 36^2 = 1296 \equiv 31\) (since \(55 \times 23 = 1265\)). Then \(13^{27} = 13^{16} \times 13^8 \times 13^2 \times 13^1 \equiv 31 \times 36 \times 4 \times 13\). Step by step: \(31 \times 36 = 1116 \equiv 16\) (\(55 \times 20 = 1100\)); \(16 \times 4 = 64 \equiv 9\); \(9 \times 13 = 117 \equiv 7\) (\(55 \times 2 = 110\)). So \(M = 7\). ✓
- \(n = 5 \times 11 = 55\); \(\varphi(n) = (5-1)(11-1) = 4 \times 10 = 40\)।
- দরকার \(3d \equiv 1 \pmod{40}\)। Try করি: \(3 \times 27 = 81 = 2 \times 40 + 1\)। তাই \(d = 27\)।
- Encrypt: \(C = 7^3 \bmod 55 = 343 \bmod 55\)। \(55 \times 6 = 330\), তাই \(C = 13\)।
- Decrypt: \(M = 13^{27} \bmod 55\)। Repeated squaring: \(13^2 = 169 \equiv 4\); \(13^4 \equiv 4^2 = 16\); \(13^8 \equiv 16^2 = 256 \equiv 36\); \(13^{16} \equiv 36^2 = 1296 \equiv 31\) (কারণ \(55 \times 23 = 1265\))। তারপর \(13^{27} = 13^{16} \times 13^8 \times 13^2 \times 13^1 \equiv 31 \times 36 \times 4 \times 13\)। ধাপে ধাপে: \(31 \times 36 = 1116 \equiv 16\) (\(55 \times 20 = 1100\)); \(16 \times 4 = 64 \equiv 9\); \(9 \times 13 = 117 \equiv 7\) (\(55 \times 2 = 110\))। তাই \(M = 7\)। ✓
Show Answerউত্তর দেখুন
- Alice sends \(A = 5^6 \bmod 23\): \(5^2 = 25 \equiv 2\); \(5^4 \equiv 4\); \(5^6 \equiv 4 \times 2 = 8\). So \(A = 8\).
- Bob sends \(B = 5^{15} \bmod 23\): \(5^8 \equiv 16\); \(5^{15} = 5^8 \cdot 5^4 \cdot 5^2 \cdot 5 \equiv 16 \cdot 4 \cdot 2 \cdot 5\); \(16 \times 4 = 64 \equiv 18\); \(18 \times 2 = 36 \equiv 13\); \(13 \times 5 = 65 \equiv 19\). So \(B = 19\).
- Alice: \(S = 19^6 \bmod 23\). \(19 \equiv -4\), \((-4)^6 = 4096 = 178 \times 23 + 2 \equiv 2\).
- Bob: \(S = 8^{15} \bmod 23 = 2^{45}\). \(2^{11} = 2048 = 89 \times 23 + 1 \equiv 1\), so \(2^{45} = (2^{11})^4 \times 2 \equiv 2\).
- Alice পাঠায় \(A = 5^6 \bmod 23\): \(5^2 = 25 \equiv 2\); \(5^4 \equiv 4\); \(5^6 \equiv 4 \times 2 = 8\)। তাই \(A = 8\)।
- Bob পাঠায় \(B = 5^{15} \bmod 23\): \(5^8 \equiv 16\); \(5^{15} = 5^8 \cdot 5^4 \cdot 5^2 \cdot 5 \equiv 16 \cdot 4 \cdot 2 \cdot 5\); \(16 \times 4 = 64 \equiv 18\); \(18 \times 2 = 36 \equiv 13\); \(13 \times 5 = 65 \equiv 19\)। তাই \(B = 19\)।
- Alice: \(S = 19^6 \bmod 23\)। \(19 \equiv -4\), \((-4)^6 = 4096 = 178 \times 23 + 2 \equiv 2\)।
- Bob: \(S = 8^{15} \bmod 23 = 2^{45}\)। \(2^{11} = 2048 = 89 \times 23 + 1 \equiv 1\), তাই \(2^{45} = (2^{11})^4 \times 2 \equiv 2\)।
Show Answerউত্তর দেখুন
Show Answerউত্তর দেখুন
- \(n = 3 \times 11 = 33\), \(\varphi(n) = 2 \times 10 = 20\). Need \(7d \equiv 1 \pmod{20}\): \(7 \times 3 = 21 = 20 + 1\). So \(d = 3\).
- Encrypt: \(C = 2^7 \bmod 33 = 128 \bmod 33\). \(33 \times 3 = 99\), so \(C = 29\).
- Decrypt: \(M = 29^3 \bmod 33\). Trick: \(29 \equiv -4 \pmod{33}\), so \(29^3 \equiv (-4)^3 = -64 \equiv -64 + 66 = 2\). \(M = 2\). ✓
- To find \(d\) an attacker needs \(\varphi(n)\), which requires factoring \(n\) into \(p\) and \(q\) — easy for 33, but practically impossible for real 2048-bit \(n\).
- \(n = 3 \times 11 = 33\), \(\varphi(n) = 2 \times 10 = 20\)। দরকার \(7d \equiv 1 \pmod{20}\): \(7 \times 3 = 21 = 20 + 1\)। তাই \(d = 3\)।
- Encrypt: \(C = 2^7 \bmod 33 = 128 \bmod 33\)। \(33 \times 3 = 99\), তাই \(C = 29\)।
- Decrypt: \(M = 29^3 \bmod 33\)। Trick: \(29 \equiv -4 \pmod{33}\), তাই \(29^3 \equiv (-4)^3 = -64 \equiv -64 + 66 = 2\)। \(M = 2\)। ✓
- \(d\) বের করতে attacker-এর \(\varphi(n)\) লাগবে, যার জন্য \(n\)-কে \(p\) আর \(q\)-তে factor করতে হবে — 33-এর জন্য সহজ, কিন্তু বাস্তবের 2048-bit \(n\)-এর জন্য কার্যত অসম্ভব।
Show Answerউত্তর দেখুন
- Compression needs patterns. Compression shrinks data by finding repeated patterns (redundancy). Good ciphertext looks completely random (high entropy) with no patterns left, so compressing after encryption saves almost nothing.
- Compression first also helps security. Removing redundancy removes the statistical patterns (like letter frequencies) that an attacker could use for cryptanalysis, so the encryption input is harder to attack.
- Compression-এর pattern লাগে। Compression data ছোট করে repeated pattern (redundancy) খুঁজে। ভালো ciphertext একদম random দেখায় (high entropy), কোনো pattern থাকে না — তাই encryption-এর পরে compress করলে প্রায় কিছুই ছোট হয় না।
- আগে compress করলে security-তেও লাভ। Redundancy সরালে সেই statistical pattern-গুলোও (যেমন letter frequency) চলে যায়, যা attacker cryptanalysis-এ কাজে লাগাতে পারত — তাই encryption-এর input attack করা কঠিন হয়।
Show Answerউত্তর দেখুন
- The attack: the attacker sends a flood of DHCP DISCOVER requests, each with a different spoofed (fake) MAC address. The DHCP server reserves an IP address for each fake "device", so its limited address pool runs out. Real clients then cannot get an IP and cannot use the network — a DoS attack on availability. Often the attacker then runs a rogue DHCP server that answers clients with attacker-controlled settings (fake gateway/DNS), enabling a man-in-the-middle position.
- One defense: DHCP snooping on the switch — only trusted ports may carry DHCP server replies, and fake server replies are dropped. (Also acceptable: port security, which limits how many MAC addresses one switch port may use, so one port cannot fake thousands of clients.)
- Attack-টা: attacker অনেকগুলো DHCP DISCOVER request পাঠায়, প্রতিটাতে আলাদা spoofed (নকল) MAC address। DHCP server প্রতিটা নকল "device"-এর জন্য একটা করে IP address আটকে রাখে, ফলে সীমিত address pool শেষ হয়ে যায়। তখন আসল client IP পায় না, network ব্যবহার করতে পারে না — এটা availability-র উপর একটা DoS attack। প্রায়ই attacker এরপর একটা rogue DHCP server চালায়, যেটা client-দের attacker-এর নিয়ন্ত্রণের setting (নকল gateway/DNS) দেয় — এতে man-in-the-middle position তৈরি হয়।
- একটা defense: switch-এ DHCP snooping — শুধু trusted port দিয়ে DHCP server-এর reply আসতে পারবে, নকল server-এর reply ফেলে দেওয়া হয়। (Port security-ও গ্রহণযোগ্য — এক switch port-এ কয়টা MAC address চলবে তা সীমিত করে, তাই এক port হাজার হাজার client সাজতে পারে না।)